Using UI
Learn how to create a resource policy in Ranger to grant the Assume_Role permissions for the user using UI.
- Sign in to Cloudera Manager.
- In the left navigation, click Clusters.
- Select the relevant Ranger cluster.
- Click the Web UI dropdown menu and click one of the Ranger Admin Web UI. The Ranger log in page displays.
- Sign in to Ranger. The Ranger home page displays.
- In the left navigation pane, select Resource Policies, and then select cm_ozone.
-
Click Add New Policy button. The Create
Policy page displays.
Figure 1. Create new policy in Ranger
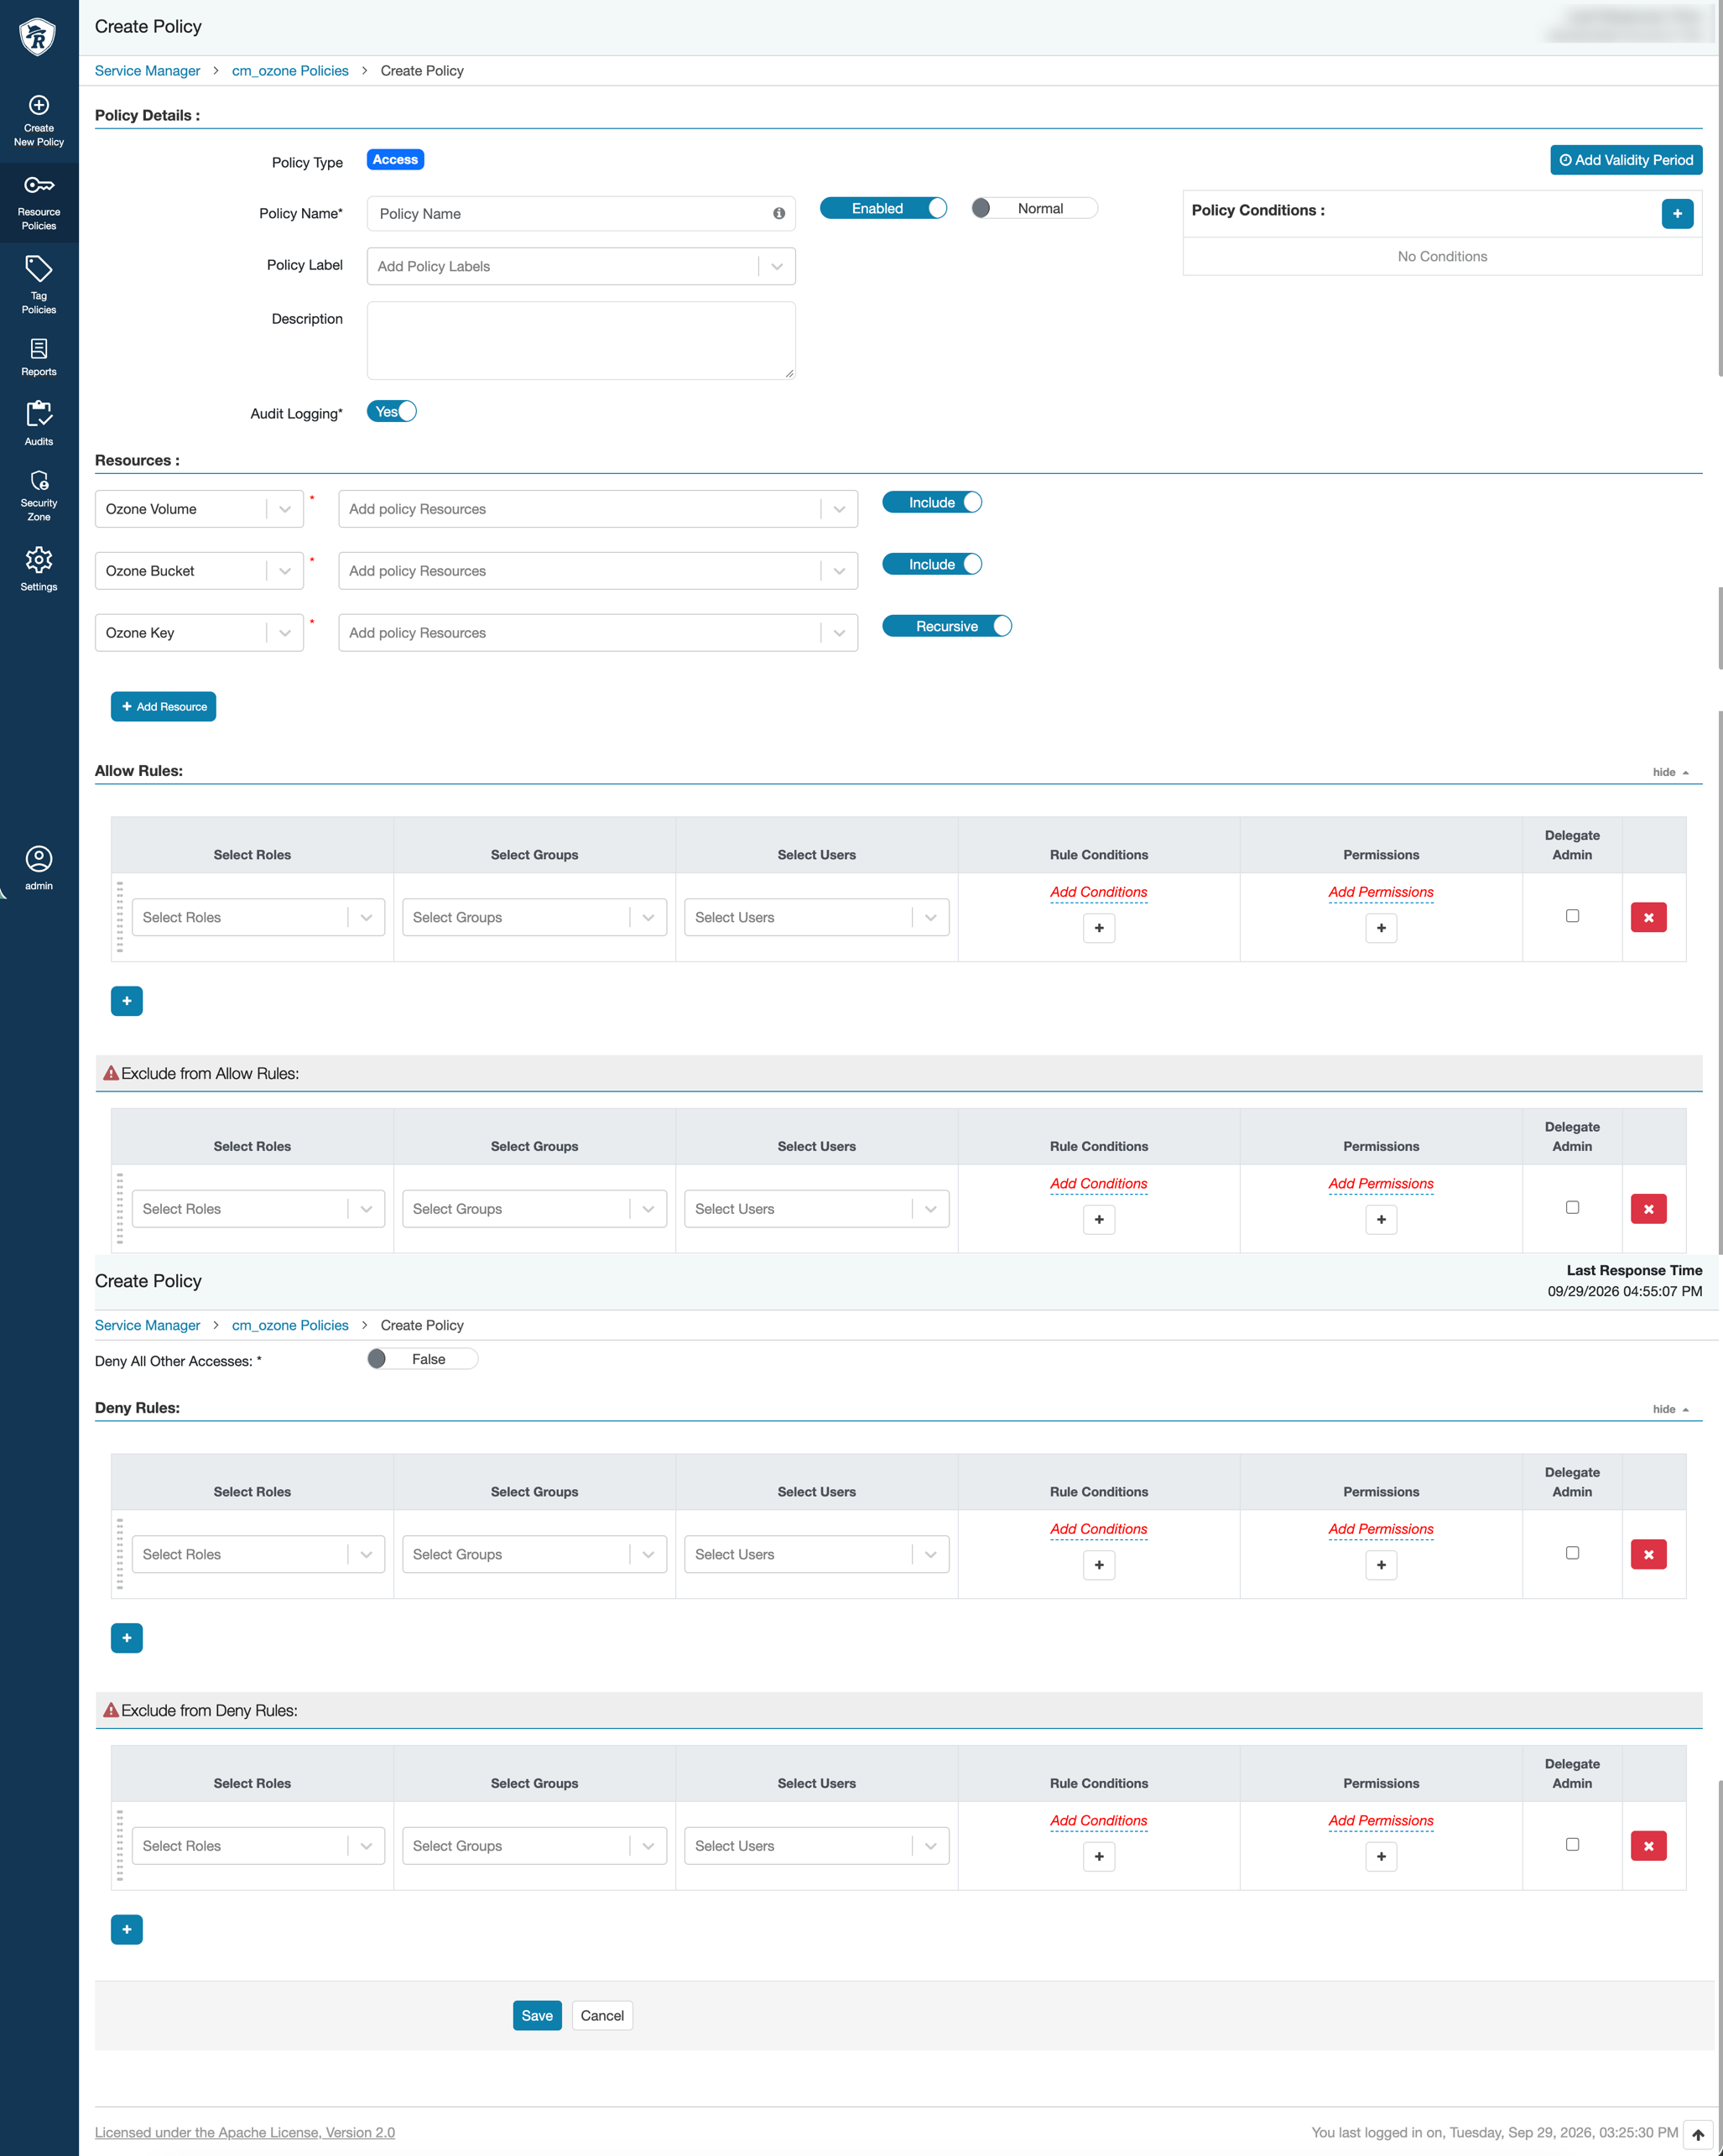
- In the Policy Name box, enter a descriptive name for the policy. For example, iceberg assume role policy.
- In the Resources section, click the Ozone Volume drop-down menu and select Role.
- In the Add policy Resources text box, enter the role name (for example, iceberg-data-all-access), wait for the list to update, and select Create [***ROLE_NAME***].
-
In the Allow Rules section, perform the following
actions:
- Under Select Users, select the service user (for example, svc-iceberg-rest-catalog).
- Under Permissions, select the plus sign (+).
-
Select the Assume_Role check box, and then
select the
check mark at the bottom of the dialog box.

- Click Save.
